So it is not the password itself that is compared with the user on the server, but the hash of that password. So our server has not stored your password anywhere. Nice, right, so where is the weak spot?
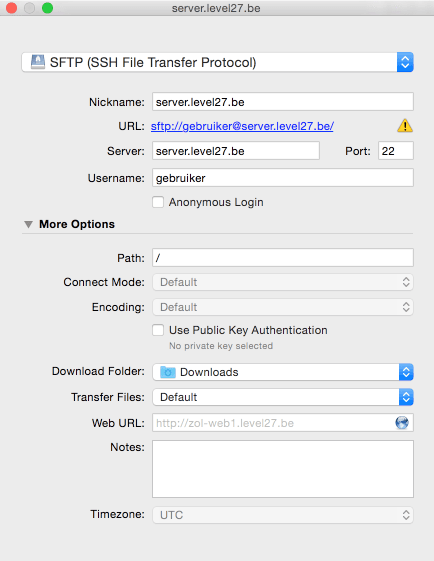
The weak spot is the user, you. Because you always tick that your FTP program should store your password. And to be able to do the dialogue with the server above, your FTP program must store the password in readable text.
It still happens that we see hackers collecting passwords this way and hacking sites on our servers. They do this via malware, spyware, viruses, …
You never store those passwords? Good for you, but even then you can have problems. Maybe you have an email somewhere with those passwords you got from your hosting provider. Or you shared those passwords with someone, e.g. a programmer working on your site. Or within your company everyone knew the FTP password, but people left your company who can still access your site. All in all, enough reason to look for a solution for the use of passwords.
Solution 2 - away with passwords
Wouldn’t it be nice if you could identify yourself to our server in an unambiguous way, without needing a password?
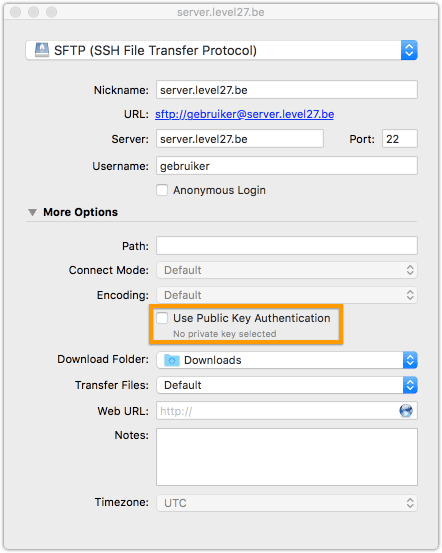
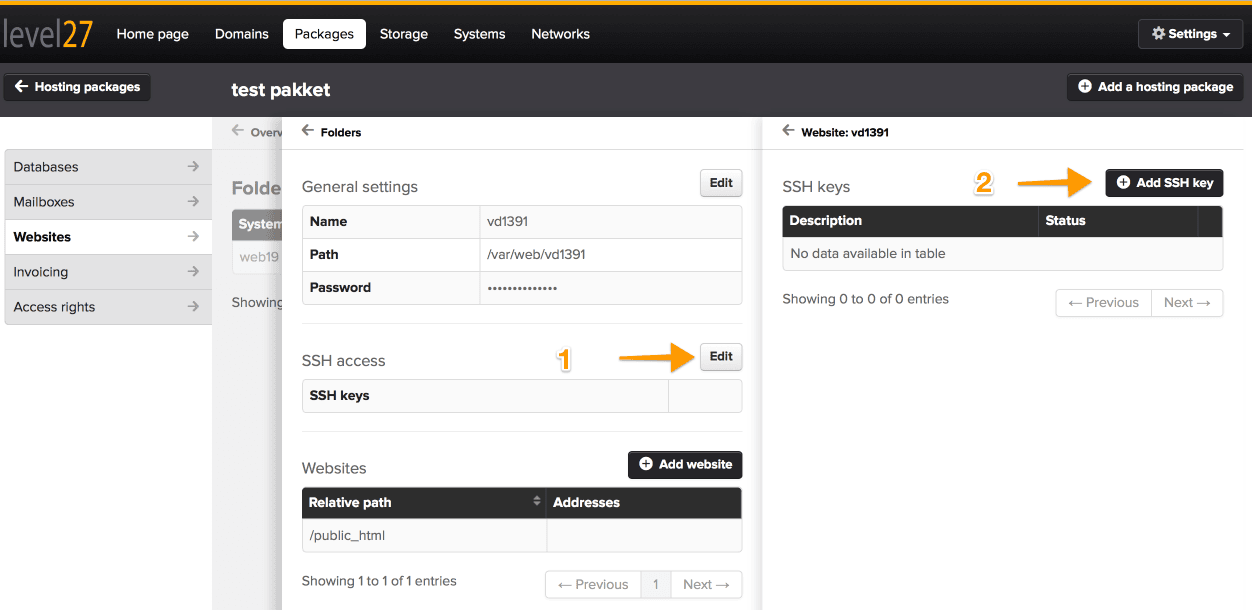
Well, that is possible with SSH. We use private and public key authentication for this. This is an advanced, yet still user friendly concept, where you work with keys on your PC.
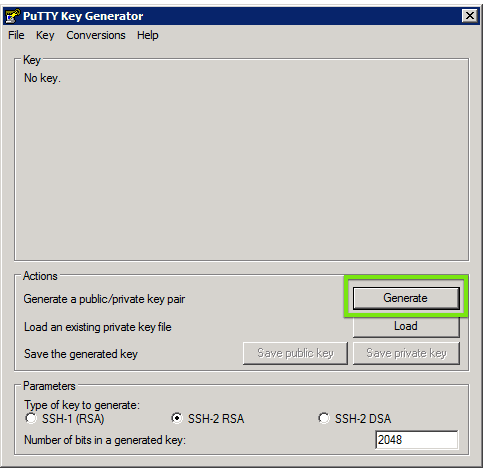
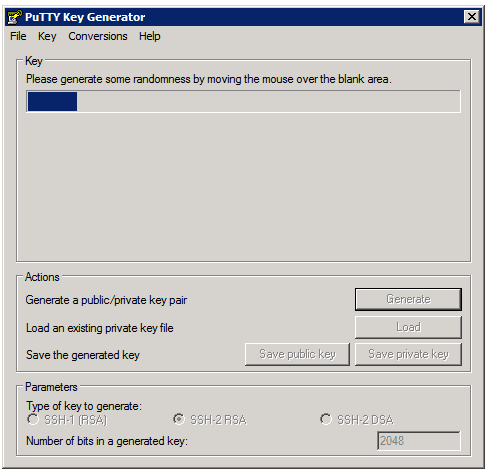
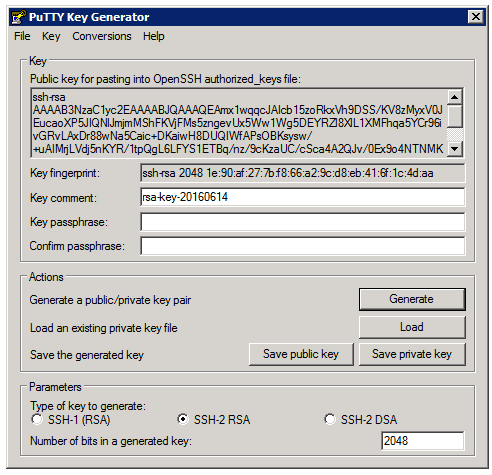
Such a key is generated completely randomly, and always comes in pairs. A private key: