ISO, what's that again?
To understand ISO, it is useful to know the difference between internal and external standards. An internal standard is a standard that an organisation sets for itself. An example of this would be that all McDonald's hamburgers must look the same.
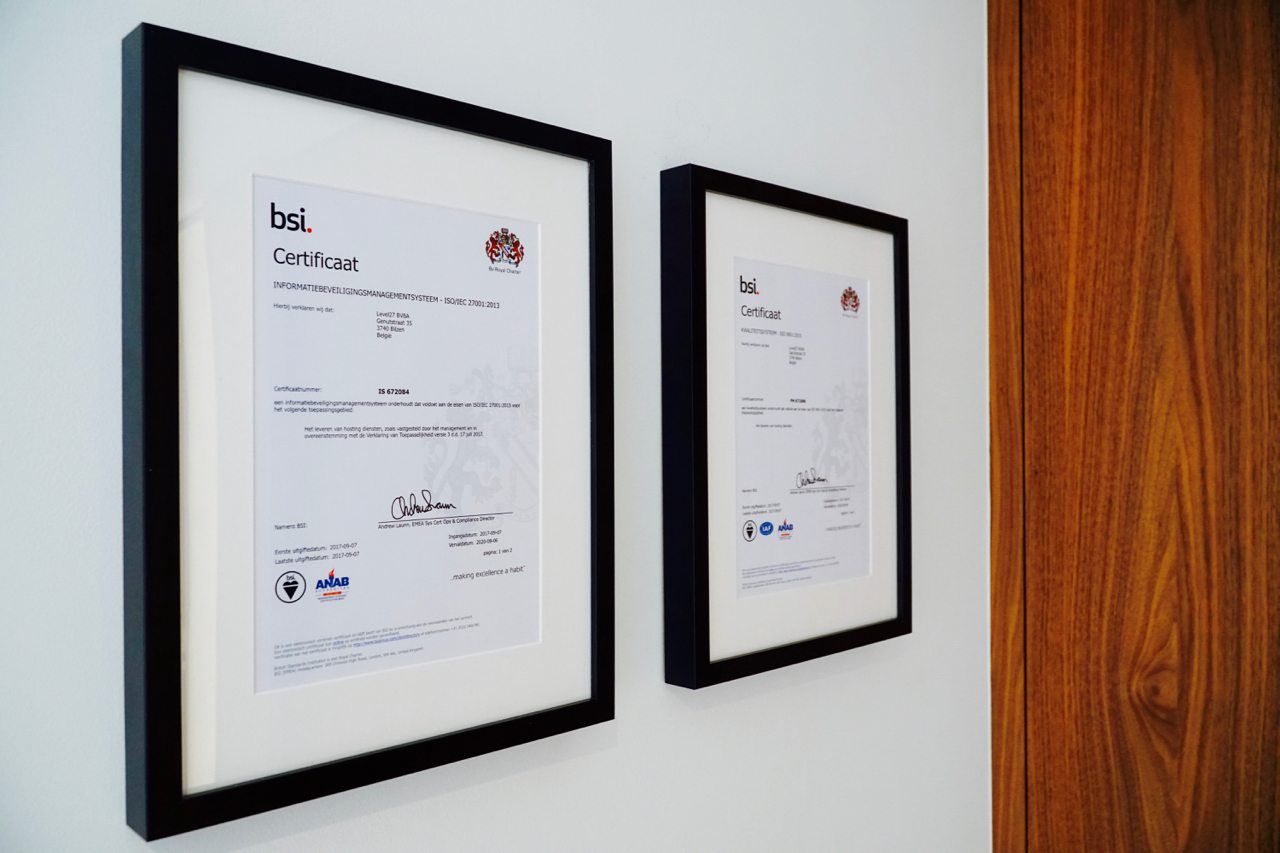
ISO, on the other hand, stands for International Organisation of Standardisation. This organisation sets external standards against which all companies can measure themselves. This allows companies to be compared with each other on the basis of these standards. In 2017, Level27 chose to obtain two certificates at once: ISO 9001 and ISO 27001.
ISO 9001
ISO 9001 is the standard for quality systems. Organisations with this certificate have a fundamental system in place that focuses on quality. To use McDonald's as an example again: not everyone likes their burgers, but their ISO 9001 certification shows that they have a system in place that ensures the quality of those burgers is consistent all over the world. Consistency of service is therefore a top priority.
ISO 27001
ISO 27001 is an information security standard, specifically relevant to the sector in which Level27 operates. This certification demonstrates that we have developed a system that guarantees the secure storage of our customers' information. Three important keywords in information security are availability, confidentiality and integrity:
- Availability may seem unrelated to security, but when it comes to hosting, it is very important that data is effectively available. Uptime is a must!
- Confidentiality is a given, which means that our customers' data is not available to others.
- Integrity means that the data we maintain is indeed correct. As an end customer, you can be sure that nothing will be changed in that data.
Identifying risks
In order to improve your internal systems, it is very important to identify risks. A risk has two characteristics: the probability of it occurring and the impact when it occurs. The risk is determined by multiplying the probability by the impact. When a risk is high, we cannot accept it and measures must be taken to address it. If we choose to accept a risk, this must of course be justified.
ISO certification obtained. What now?
After a great deal of work, time and resources, we achieved our first certification in 2017. But of course, we couldn't just throw all our ISO principles out the window after that. During an audit, the auditor may note a number of findings:
- An opportunity for improvement
- A non-critical deviation
- A critical deviation
In the event of a critical deviation, no certificate will be issued. For opportunities for improvement and non-critical deviations, a check is carried out during the audit the following year to see whether improvements or adjustments have been made. Moreover, an organisation such as ours is constantly changing internally, especially because the focus on improvement within Level27 is very strong.
That is why new action points are added every year. These are monitored throughout the year in an improvement process in ClickUp, our task and planning tool. In addition, regular meetings are scheduled with KVGM and an internal audit is carried out for each standard every year in collaboration with them, so that we are fully prepared when the external auditor visits again.